Automotive
Downtime and Data Exposure Hit Your Bottom Line Directly
Dealerships that finance or lease vehicles fall under the FTC Safeguards Rule. Manufacturers and suppliers face customer security questionnaires and plant-floor risk. USDG builds the program and can serve as your Qualified Individual.
FTC Safeguards Rule Compliance
Written program, risk assessment, and monitoring in place
A Qualified Individual
A named person to oversee your program; we can be that person
Monitoring for Dealership & Plant Systems
DMS, finance office, and production systems watched around the clock
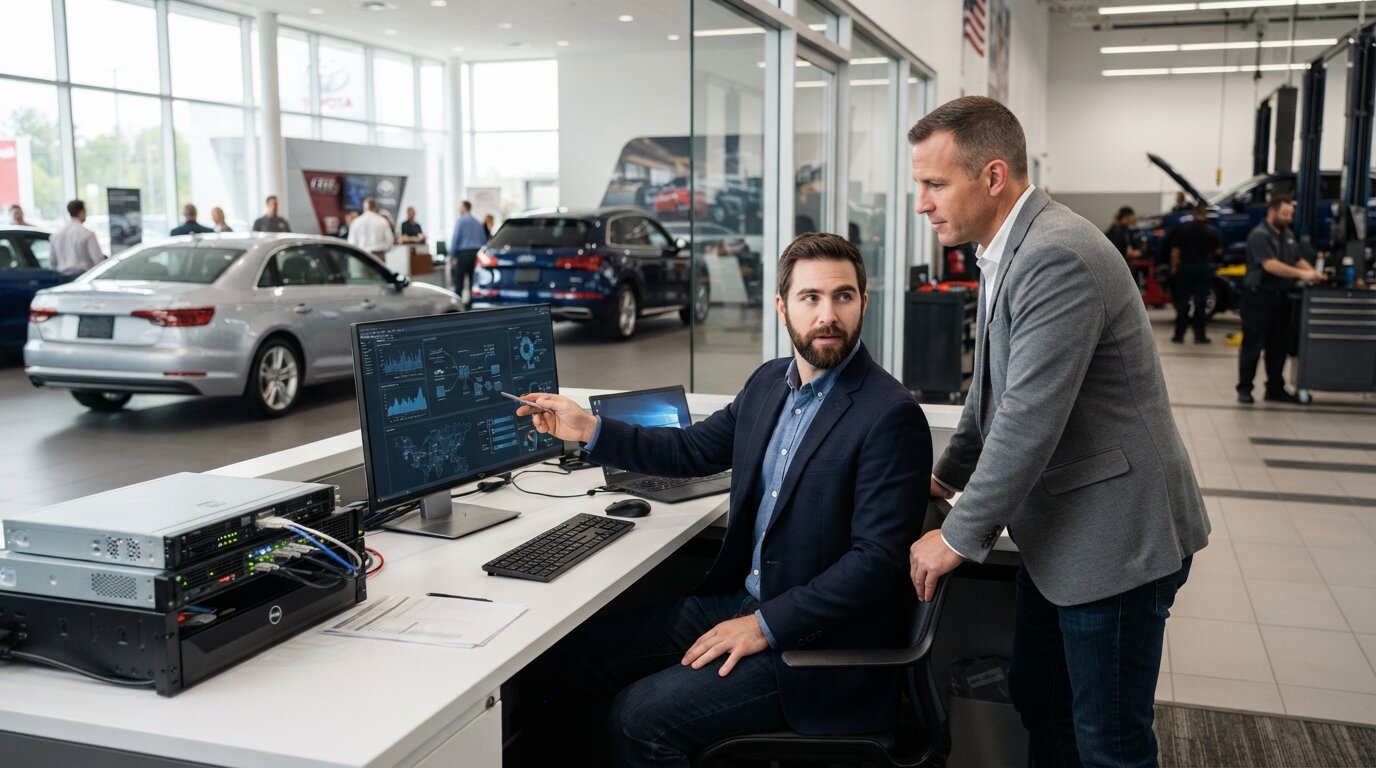
It's a Saturday, the busiest sales day of the week, and the dealer management system goes down. Deals stall, financing can't be submitted, and customers are standing in the showroom.
Who This Is For
Engineered for Dealerships, Plant Floors & Automotive Supply Chains
Core technical and operational capabilities built to keep vehicles moving, protect production continuity, reduce costly downtime, and maintain quality across dealerships, plant floors, and complex automotive supply chains.
Dealerships that finance or lease vehicles
Automotive retail groups, franchised dealerships, and independent finance centers handling consumer credit applications, title data, and NPI under FTC jurisdiction.
Manufacturers and suppliers with plant-floor systems
Tier-1 and Tier-2 automotive component suppliers, parts fabricators, and assembly facilities balancing OT/IT integration, robotics, and production uptime.
Operations answering customer or partner security questionnaires
Commercial fleet operators, leasing companies, and vendors undergoing stringent OEM, bank, and lender cybersecurity audits with tight deadlines.
Automotive Security Priorities
What Matters Most in Automotive
Core technical, financial, and regulatory safeguards required to keep deals moving, plants running, and examiners satisfied.
1. Protecting customer financial data in the finance office and DMS
Encryption, credit application redaction, and strict role-based access controls for F&I desks to isolate sensitive non-public personal information (NPI).
2. Keeping deal processing and production systems running
High-availability safeguards and continuous telemetry so DMS crashes, plant disruptions, or ransomware never halt vehicle delivery or production line work.
3. Overseeing the vendors your dealership or plant depends on
Rigorous third-party risk management covering CRM vendors, DMS providers, parts distributors, and floor-plan inventory software platforms.
4. Meeting FTC notice deadlines if customer data is exposed
Turnkey incident protocols ensuring mandatory statutory FTC notification within 30 days of discovering a breach affecting 500 or more consumers.
5. Answering security questionnaires from lenders, OEMs, and customers
Defensible documentation, audit-ready compliance evidence binders, and executive attestations required to secure lender floor plans, maintain OEM franchise agreements, and pass institutional audits.
Integrated Defense Suite
Our Services for Automotive Businesses
Modular components engineered to function harmoniously as your outsourced security and compliance department.
Cyber Risk & Compliance Assessment
Comprehensive DMS audit, financial data discovery, perimeter scans, and physical security analysis tailored to showroom and floor-plan risks.
Managed GRC
Ongoing Safeguards rule maintenance, vendor oversight audits, automated policy tracking, and dealership employee compliance logs.
Virtual CISO & Advisory
Designated Qualified Individual representation for lenders, boards, and regulators. Executive-level guidance without executive headcount overhead.
Continuous Cybersecurity Management
24/7 real-time monitoring of dealership sales networks, finance workstations, and plant production lines with rapid threat isolation.
Incident Response & Readiness
Guaranteed SLA response times, immediate threat eradication, forensic reporting, and FTC breach notification execution to avoid sanctions.
Statutory Defense & Mandate Alignment
Regulation & FTC Safeguards Rule Mapping
FTC Safeguards Rule Requirement
How USDG Delivers It
Written risk assessment
Identification of threats, asset cataloging, and operational vulnerability prioritization.
Cyber Risk & Compliance Assessment
Written information security program, vendor oversight, staff training
Formal Safeguards policy framework, dealership vendor evaluations, and mandatory employee cybersecurity hygiene modules.
Managed GRC
A single Qualified Individual
Statutorily designated oversight role responsible for presenting formal annual risk evaluations to dealership ownership or boards.
Virtual CISO & Advisory
Continuous monitoring or annual testing, MFA
24/7 endpoint detection, rigorous MFA rollouts for DMS access, and continuous penetration or vulnerability testing.
or vulnerability testing. Continuous Cybersecurity Management
Written incident response plan, FTC notice at 500+ consumers
Pre-drafted, tested containment playbooks and legally defensible electronic notice filings to the FTC within 30 days.
Incident Response & Readiness
Clear Answers
Frequently Asked Questions
Does the Safeguards Rule apply to us if we don't originate loans?
If your dealership arranges financing or leasing for customers, it likely applies. We confirm this in the free assessment.
Can you work with our DMS provider?
Yes. We work alongside your existing systems and vendors.
Find Out What the Safeguards Rule Requires of You
A security assessment costs you nothing but a conversation. Let's make sure your dealership systems, customer financing data, and business reputation are protected.
- No sales pressure
- 100% confidential NDA
- Actionable findings roadmap